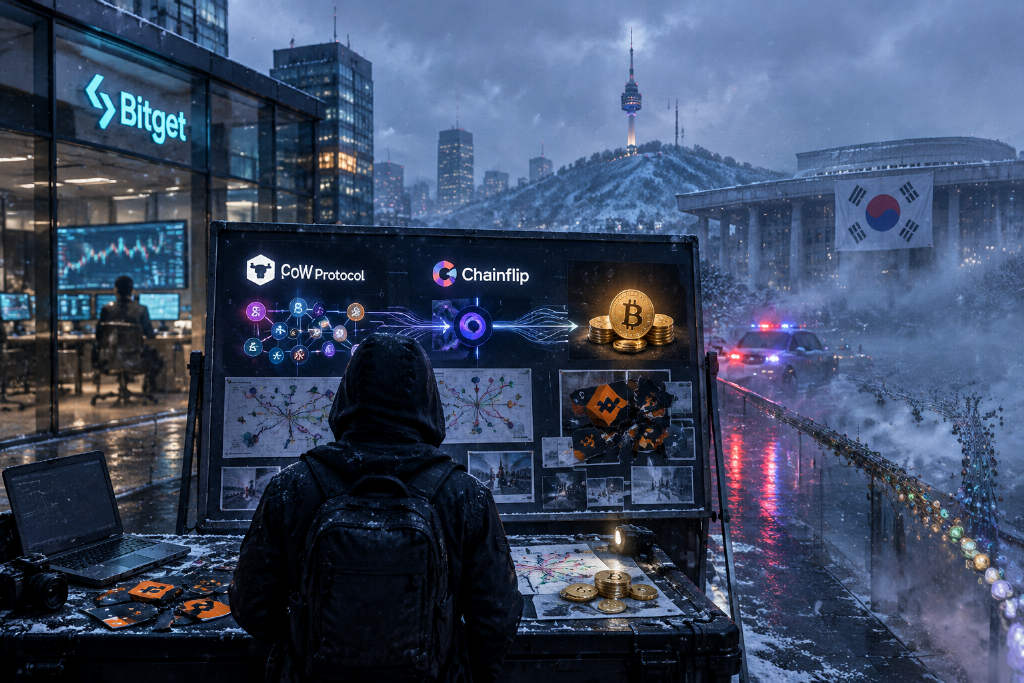
SlowMist2026-09-30 03:05:09SlowMist founder says North Korean hackers used CoW Protocol and Chainflip to move funds into BTCSlowMist founder Yu Xian said on Sept. 30 that the firm’s TrackAgent system identified a laundering route used by North Korean hackers to process funds stolen from Bitget. According to his post, the actors combined CoW Protocol with Chainflip in an automated workflow that started with an order on CoW Protocol and ended with the assets being bridged and converted into BTC. Yu Xian said the script set the payout address of a CoW Protocol order to a pre-arranged Chainflip deposit-related contract address. Once the order was filled, the cross-chain step on Chainflip could be completed and the funds would be swapped into bitcoin. He also shared one example transaction in which the recipient address, 0xcEAE932A8bEE3a81a681A59890cb26d3110FDb65, corresponded to a Chainflip Deposit Contract. Chainflip records tied that flow to a final BTC address, bc1qa0rjjhyu9pg3adgpel4v7dct6a8606az863jyh. Yu Xian added that Chainflip had been blocking North Korean laundering attempts, but the group used automated scripts to split funds into many pieces and quickly shifted to other cross-chain routes when risk controls or blocking measures appeared. He described the process as an "evolving laundering operation."310
SlowMist2026-09-20 09:31:45SlowMist founder flags ComeCome app after FomoPeek wallet-theft attackSlowMist founder Yu Xian said a food-delivery app called ComeCome, operating through comecome.icu, was found using a method similar to the earlier FomoPeek app poisoning incident. According to his disclosure, FomoPeek versions 1.1 to 1.2 contained a malicious SDK with eight iOS kernel exploit paths, allowing the code to choose an attack method based on device model and system version. Known affected iOS versions span iOS 12 to 18.7 and 26 to 26.1. Once the attack succeeds, it can break out of the iOS sandbox and steal assets from crypto wallets. Yu Xian also warned that the same kind of threat may extend to iPad and Mac devices. He advised users to update to the latest iOS release immediately and stay highly cautious about apps from unknown sources.440
SlowMist2026-08-09 11:21:35SlowMist's Cos Says No Need to Warn About Replay Attacks for Failed BIP-110 ForkOdaily reported that Cos, also known as Yu Xian from SlowMist, said in a post on X that there is no need to keep reminding users about replay attacks tied to the failed BIP-110 fork. The brief update did not include additional technical explanation, background on the fork, or any follow-up details beyond that statement. Based on the source material provided, the remark was limited to that point and did not expand on risk scope, timing, or related mitigation steps.1960
Claude Code2026-07-18 02:12:32SlowMist founder flags poisoning risk in Claude Code and Grok Build CLIOdaily reported that SlowMist founder Yu Xian reposted a warning on X about a potential poisoning attack against Claude Code and published his own analysis covering poisoning risks tied to both Grok Build CLI and Claude Code CLI. According to the analysis, Grok Build CLI lacks a unified security model, with different code paths relying on different trust assumptions. That gap could let attackers use a malicious project configuration file to run arbitrary commands without the user’s knowledge. Researchers also built a test environment and found that on macOS, if Claude Code is affected, running a specific test command could launch the local Calculator app, which they said demonstrates a potential command execution risk. If such an attack succeeds, it could lead to the theft of API keys for AI services such as Claude and OpenAI, cloud credentials for AWS, Alibaba Cloud and Tencent Cloud, unauthorized access to servers and data, code repository tampering, backdoor insertion, and the use of a local machine as a pivot point into an enterprise internal network. The report added that the related vulnerability has existed for one year.1850
SlowMist2026-07-18 02:12:53SlowMist founder flags poisoning attack risks in Grok Build CLI and Claude Code CLISlowMist founder Yu Xian reposted a thread on X about potential poisoning attack risks tied to Claude Code and published his own analysis covering Grok Build CLI and Claude Code CLI. According to the analysis, Grok Build CLI does not apply a single, consistent security model across its code paths. Different trust assumptions in different paths may open gaps that attackers can exploit. A malicious project configuration file could let an attacker run arbitrary commands without the user realizing it, then steal API keys, cloud credentials, or take control of a local device. Researchers also built a test environment and found that on macOS, if Claude Code is affected, running a specific test command can trigger the local Calculator app to open. That result was presented as evidence of a potential command execution risk. If such an attack succeeds, the fallout could extend beyond local execution. The analysis says attackers may steal API keys for AI services including Claude and OpenAI, causing billing losses, obtain credentials for AWS, Alibaba Cloud, and Tencent Cloud to access servers and data, tamper with code repositories to implant backdoors, or use the compromised local machine as a pivot into an enterprise internal network. The related vulnerability is said to have existed for one year.1860